

Modern businesses rely on services they don’t run themselves. The company data is held or touched by the cloud platform, payment processor, billing tools, marketing software and outsourced support. Each one is convenient. Each one becomes part of the business’s attack surface.
When a third-party provider is compromised, it’s often the customers it serves that bear the brunt, whether or not they did anything wrong. This is why assessing a provider’s security before signing, and checking up on it after, has become a basic part of running a responsible business.
Start With an Inventory of What You Actually Use
Many organisations cannot list every outside service connected to their data. Teams adopt tools on their own, trial accounts become permanent, and integrations quietly accumulate. A review cannot protect anything that has not been identified.
A practical first step is a simple inventory that records each provider, what it is used for, who owns the relationship, and what data it can access. Even a basic spreadsheet turns an invisible problem into something a business can manage, and it often uncovers tools that nobody remembers approving.
Rank Providers by What They Can Reach
Not every provider deserves the same level of scrutiny. A tool that schedules internal meetings poses a different risk than a platform that stores customer records or has administrative access to company systems.
Sorting providers into tiers based on data sensitivity and operational importance keeps the process realistic. The highest tier, covering systems that handle regulated data or whose failure would stop the business, gets a thorough review. Lower tiers get lighter checks. This approach focuses limited time where the exposure is greatest.
Ask Specific Questions, Not General Ones
A provider that says it takes security seriously has not told you much. Useful questions are concrete. How is data encrypted in storage and in transit? Who at the provider can access customer data, and how is that access controlled and logged? How quickly will you be notified if there is an incident? Where is data stored, and which other companies does the provider rely on to deliver the service?
Independent assurance reports and recognised certifications can help, since they show that an outside party has examined the provider’s controls. They should be read, not just collected, because the scope of a report matters as much as its existence.
Put Security Expectations Into the Contract
Verbal promises are not enough when a security incident occurs. A well-written contract should clearly explain how and when the provider must report an incident, who is responsible for responding to it, and how the two parties will work together to limit its impact. It should also specify what happens to your data when the contract ends and give you the ability to review relevant security reports or evidence periodically.
For businesses in regulated sectors such as healthcare and financial services, these agreements should also account for the legal and regulatory requirements that apply to the data being handled. Working with a third-party provider does not automatically remove a business’s own compliance responsibilities, so it is important to establish these expectations before sharing sensitive information.
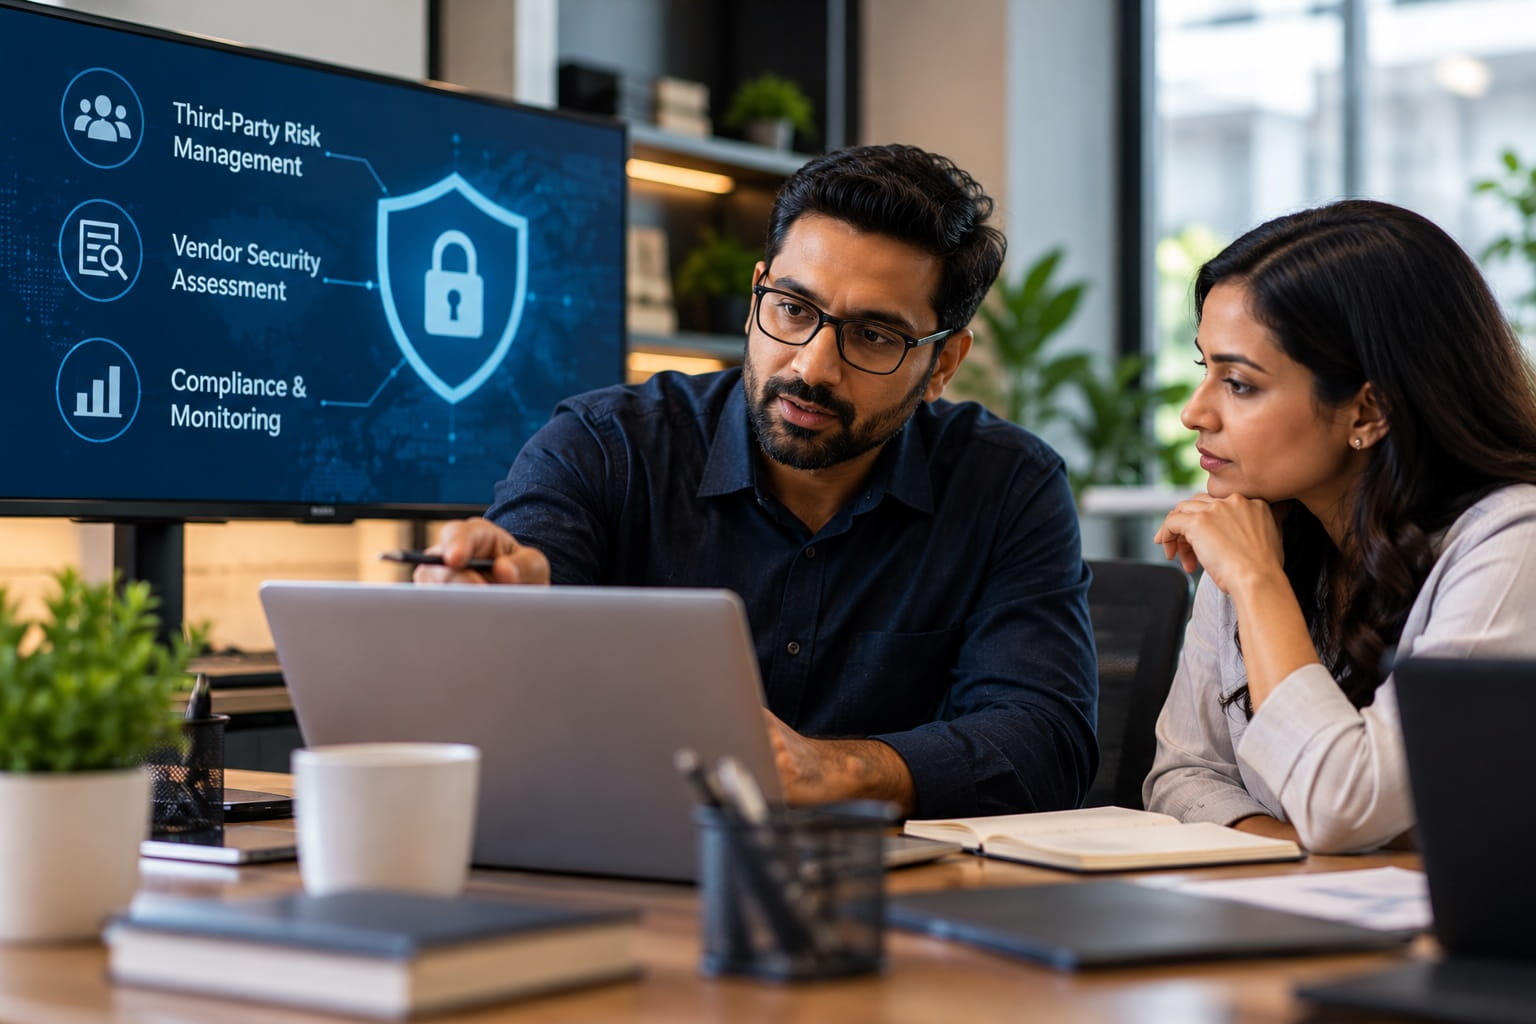
Monitor Providers Over Time, Not Just at Signing
A review that happens once and is never revisited goes stale. Providers change their infrastructure, add subcontractors, and experience incidents. A relationship that was low risk at signing can become high risk as the business sends more data through it.
Periodic check-ins keep the picture current. For the most important providers, that may mean an annual review of updated security reports and a look at any incidents they have disclosed. Paying attention to public security news about key providers is a low-effort way to catch problems early.
Control Access and Plan for Exit
Many third-party incidents happen through access that was granted and never removed. Integrations that keep broad permissions, shared accounts used by outside teams, and credentials left active after a project ends all create unnecessary exposure.
Granting providers only the access they need, using individual accounts with multi-factor authentication, and removing access promptly when a relationship ends all reduce risk. It also helps to plan for an exit in advance, including how data will be returned or deleted and how operations would continue if a critical provider becomes unavailable.
How Mindcore Technologies Helps Businesses Manage Third-Party Risk
Mindcore Technologies provides IT consulting, managed IT services and cybersecurity support to businesses. According to the company, its services include IT services in Birmingham, cybersecurity, compliance support and IT consulting to help organisations assess technology risks, strengthen access controls and develop security review processes.
With more than 30 years of experience, Mindcore Technologies helps businesses take a practical, risk-based approach to managing third-party providers, tailored to their operational needs and compliance requirements.
Conclusion
A business cannot outsource its accountability for the data it holds. Taking inventory of the providers it uses, ranking them by risk, asking specific security questions, writing expectations into contracts, and monitoring relationships over time give a business a defensible way to rely on outside services. The process does not need to be elaborate to be effective. It needs to be consistent and focused on the providers that matter most.
Editorial Note
This article was developed in collaboration with Mindcore Technologies and is intended for general informational purposes.